MALWARE ANALYSIS
Understand the Threat. Stop the Attack.
Expert-led malware analysis combining static and dynamic analysis, behavioral investigation and reverse engineering to understand malicious software, identify indicators of compromise and support effective threat response.
From Suspicious Files to Actionable Threat Intelligence
Malware can hide its true behavior through obfuscation, encryption, packing and sophisticated execution techniques. Simply detecting a malicious file is often not enough to understand the threat or determine its potential impact.
Our Malware Analysis services investigate suspicious files and malicious code to uncover how they operate, what they target and how they communicate—providing security teams with actionable intelligence for detection, containment and remediation.
What We Do
We analyze suspicious files, executables, scripts and malicious payloads to understand their structure, behavior and capabilities.
Our analysts combine static analysis, dynamic analysis and reverse engineering techniques to investigate malware and extract meaningful indicators of compromise.
How It Helps Your Business
Malware analysis helps organizations understand the nature and impact of a suspected threat and strengthen detection capabilities.
Our findings provide security teams with actionable intelligence that can be used to identify related activity across their environment and improve defensive controls.
How Our Malware Analysis Works
A structured analysis lifecycle designed to identify, understand and contain malicious activity.
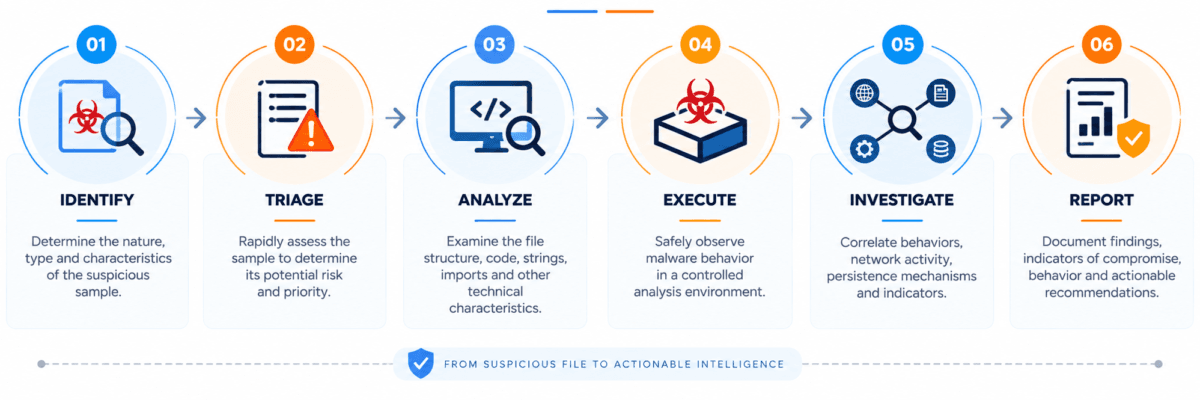
MALWARE ANALYSIS SCOPE
Our analysis can be tailored to the type of malware, sample and investigation requirements.
Static Malware Analysis
Examine malware without executing it to understand its structure, metadata, strings, imports and other technical characteristics.
Dynamic Malware Analysis
Execute suspicious samples within an isolated environment to observe their real-world behavior.
Behavioral Analysis
Investigate processes, file modifications, registry changes, persistence mechanisms and system activity.
Network Analysis
Analyze network communications, domains, IP addresses, URLs and other external connections associated with the malware.
Reverse Engineering
Analyze executable code and program logic to understand functionality, capabilities and execution flow.
Obfuscation & Packing Analysis
Investigate packed, encrypted or obfuscated samples to uncover hidden functionality and malicious logic.
Indicator of Compromise Extraction
Identify hashes, domains, IP addresses, URLs, filenames, registry keys and other indicators associated with the threat.
Malware Family Identification
Analyze technical characteristics and behavioral patterns to assist in identifying related malware families or variants.
Go Beyond Detection. Understand the Malware.
Security tools can identify suspicious files, but understanding what malware actually does requires deeper analysis.
Our malware analysis services provide technical insight into malicious code and behavior, helping your security team understand the threat, identify affected systems and strengthen detection and response capabilities.
- Static malware analysis
- Dynamic malware analysis
- Behavioral analysis
- Reverse engineering
- Network behavior analysis
- Obfuscation analysis
- Persistence analysis
- IOC extraction
- Malware family analysis
- Threat intelligence enrichment
- Detection recommendations
- Technical reporting
TESTIMONIAL
The malware analysis provided us with a much clearer understanding of the threat, including its behavior and indicators, allowing our security team to improve detection and response.
REAL-WORLD MALWARE ANALYSIS
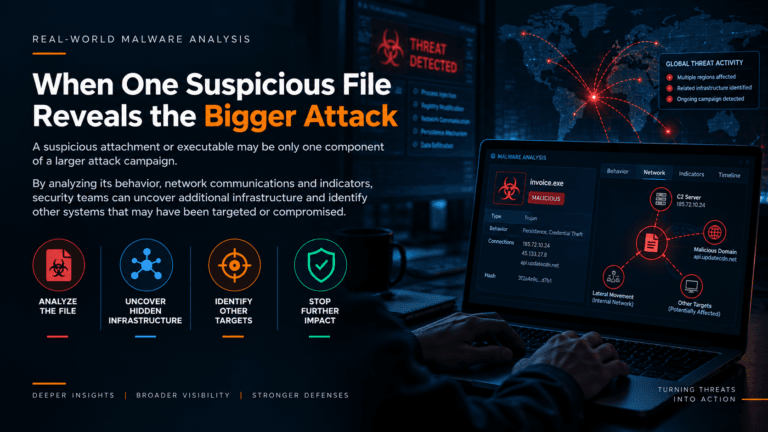
When One Suspicious File Reveals the Bigger Attack
Frequently Asked Questions
What is Malware Analysis?
Malware Analysis is the process of examining suspicious or malicious software to understand its structure, behavior, capabilities and potential impact.
What types of malware can you analyze?
Depending on the engagement, analysis can cover executables, scripts, documents, ransomware, trojans, information stealers, remote access tools and other suspicious payloads.
Do you perform static and dynamic analysis?
Yes. Malware can be examined both without execution through static analysis and within a controlled environment through dynamic analysis.
Do you perform reverse engineering?
Yes. Reverse engineering can be performed when deeper analysis of an executable’s functionality or execution logic is required.
Can you extract Indicators of Compromise?
Yes. Analysis can identify indicators such as file hashes, domains, IP addresses, URLs, filenames, registry keys and other relevant artifacts.
Can malware analysis support incident response?
Yes. Malware analysis can provide technical intelligence that helps incident responders understand the threat, identify related activity and support containment.
Can you analyze unknown malware?
Yes. Unknown or previously unidentified samples can be investigated based on their technical characteristics and observed behavior.
Is malware analysis performed in a safe environment?
Malware analysis should be performed within controlled and isolated analysis environments designed to prevent malicious samples from affecting production systems.