INCIDENT RESPONSE
Respond Fast. Contain the Threat. Recover with Confidence.
Our Incident Response services help organizations respond to ransomware, malware infections, account compromise, data breaches and other security incidents through rapid investigation, containment, eradication and recovery support.
From Security Incident to Controlled Recovery
When a cybersecurity incident occurs, every minute can matter. Delayed investigation or ineffective containment can allow attackers to maintain access, spread across systems and increase the impact on your organization.
Our Incident Response team provides structured support to identify what happened, determine the scope of compromise, contain the threat and guide your organization through recovery.
What We Do
We investigate cybersecurity incidents to understand the attack, identify affected systems and determine how the threat entered and moved through the environment.
Our response process combines incident investigation, digital evidence analysis, threat intelligence and technical containment.
How It Helps Your Business
Our Incident Response services help organizations reduce the impact of security incidents, contain active threats and restore affected systems in a controlled manner.
We provide actionable findings that help security teams understand the incident and strengthen defenses against similar attacks.
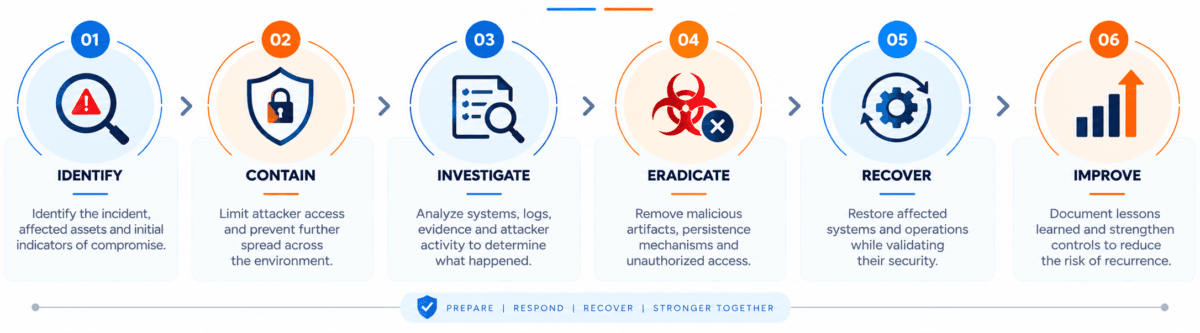
How Our Incident Response Works
A structured response lifecycle designed to contain threats and restore business operations.
INCIDENT RESPONSE SCOPE
Our response capabilities can be tailored to the nature, severity and scope of the incident.
Ransomware Incident Response
Investigate ransomware activity, identify affected systems, support containment and assist with recovery planning.
Malware Incident Response
Investigate malware infections, determine affected systems and identify indicators associated with the attack.
Data Breach Investigation
Investigate suspected unauthorized access and determine the systems, accounts and data potentially affected.
Account Compromise Response
Investigate compromised credentials and suspicious account activity while supporting containment and access recovery.
Business Email Compromise
Investigate suspicious email activity, compromised accounts, fraudulent communications and related attacker activity.
Network Intrusion Investigation
Analyze network activity and system evidence to identify unauthorized access and attacker movement.
Endpoint Incident Investigation
Examine affected endpoints to identify malicious processes, files, persistence mechanisms and other evidence.
Cloud Incident Response
Investigate suspicious activity across cloud identities, workloads, services and infrastructure.
Threat Containment
Support isolation of affected systems, blocking of malicious infrastructure and removal of attacker access.
Post-Incident Analysis
Document the incident timeline, root causes, findings and recommendations to strengthen future resilience.
When Every Minute Matters, Respond With Expertise
Cybersecurity incidents can escalate quickly. Attackers may establish persistence, move laterally, compromise additional accounts or disrupt critical systems.
Our incident response specialists help organizations move from uncertainty to a structured response by combining technical investigation, evidence analysis and containment expertise.
- Incident identification and triage
- Threat containment
- Malware investigation
- Digital evidence analysis
- Attack timeline reconstruction
- Compromise assessment
- Threat actor activity analysis
- IOC identification
- Root cause analysis
- Eradication support
- Recovery guidance
- Post-incident recommendations
TESTIMONIAL
The Incident Response team helped us quickly understand the scope of the incident, contain the affected systems and establish a clear path toward recovery.
REAL-WORLD INCIDENT RESPONSE
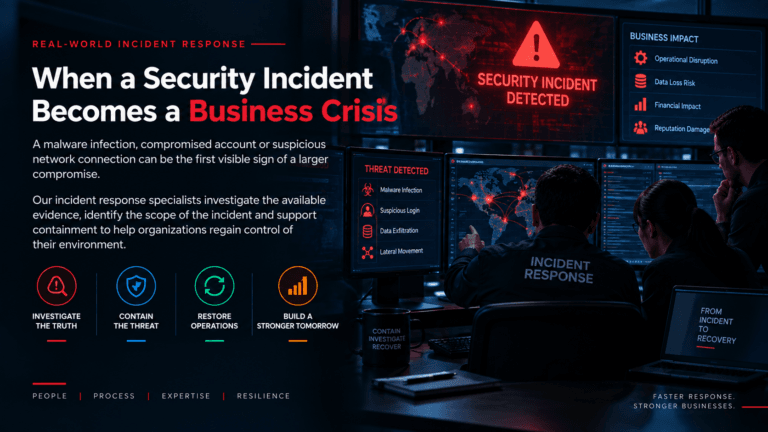
When a Security Incident Becomes a Business Crisis
FREQUENTLY ASKED QUESTIONS
What is Incident Response?
Incident Response is the structured process of identifying, containing, investigating, eradicating and recovering from a cybersecurity incident.
When should we engage an Incident Response team?
Incident Response support can be engaged when an organization suspects or confirms events such as ransomware, malware infection, unauthorized access, account compromise, data breach or other significant security incidents.
Do you respond to ransomware attacks?
Yes. Ransomware response can include incident triage, containment, investigation, compromise assessment and recovery support.
Can you determine how an attacker entered our environment?
Where sufficient evidence is available, our investigation can analyze logs, endpoints, network activity and other artifacts to help determine the initial access vector and attack path.
Do you perform digital forensics during incident response?
Yes. Digital forensic analysis can be incorporated when evidence preservation and deeper investigation are required.
Can you identify affected systems?
Our investigation can help identify potentially compromised endpoints, servers, accounts, applications and other infrastructure based on available evidence.
Do you provide a detailed incident report?
Yes. Reports can document the incident timeline, affected assets, findings, indicators, attack techniques, root causes and recommended corrective actions.
Do you help prevent similar incidents in the future?
Yes. Post-incident recommendations can identify security gaps and improvements that can help reduce the risk of recurrence.
RELATED SERVICES
RIEG
Identify and validate vulnerabilities before attackers can exploit them.
VAPT
Identify and validate vulnerabilities before attackers can exploit them.
Security Operations Center
Evaluate your network architecture, controls and exposure to security threats.