PCI DSS COMPLIANCE
Secure Payment Card Data. Strengthen Compliance. Reduce Risk.
Build a security program aligned with PCI DSS requirements to protect cardholder data, identify security gaps, strengthen payment environments and maintain ongoing compliance.
From Payment Security Gaps To Compliance
Payment card environments face continuous security threats, from vulnerable applications and exposed systems to weak access controls and insecure payment workflows.
Our PCI DSS consulting services help organizations assess their cardholder data environment, identify compliance gaps and implement security measures designed to protect payment card information.
We combine compliance expertise with technical security assessments to help organizations move from compliance requirements to practical security improvements.
What We Do
We help organizations understand their PCI DSS obligations, define the Cardholder Data Environment (CDE), identify security gaps and establish appropriate controls.
Gap assessments, risk identification, technical security testing, policy and documentation support, remediation guidance and compliance readiness.
How It Helps Your Business
A structured PCI DSS program helps organizations protect cardholder data and strengthen the security of payment-related systems.
It provides greater visibility into security gaps, improves control effectiveness and helps teams prepare for PCI DSS assessments.
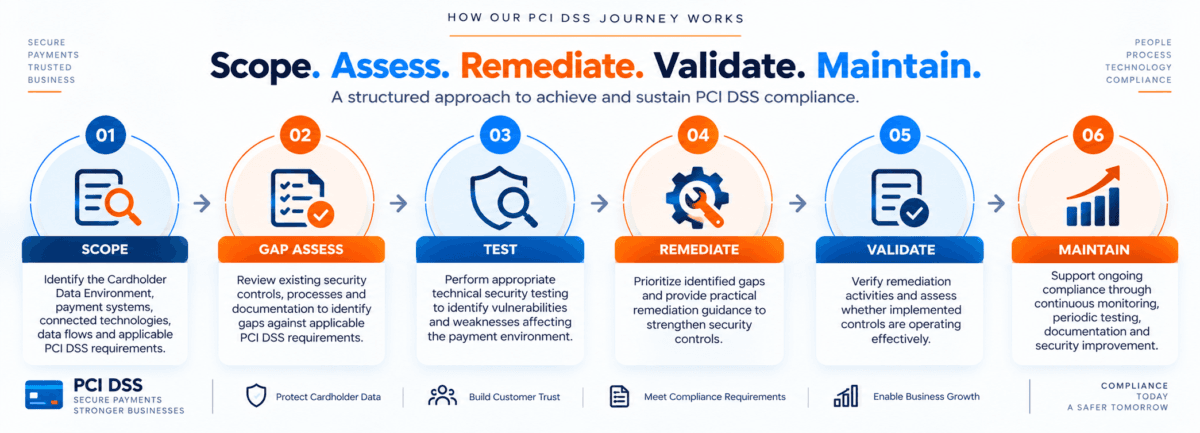
How Our PCI DSS Journey Works
Scope. Assess. Remediate. Validate. Maintain.
PCI DSS COMPLIANCE SCOPE
PCI DSS compliance depends on the systems, processes and technologies involved in storing, processing or transmitting payment card data.
Cardholder Data Environment
Identify systems and components that store, process or transmit cardholder data.
Network Security
Assess network architecture, segmentation, security configurations and controls protecting the payment environment.
Access Control
Review authentication, authorization, privileged access and user access management.
Application Security
Assess payment applications, web applications and APIs for security weaknesses.
Data Protection
Evaluate mechanisms used to protect cardholder data during storage and transmission.
Vulnerability Management
Review vulnerability management processes, patching and security testing activities.
Logging & Monitoring
Assess security logging, monitoring and mechanisms used to identify suspicious activity.
Security Policies & Procedures
Review security policies, procedures, responsibilities and operational processes supporting PCI DSS requirements.
Go Beyond the Checklist With Technical Security Validation
PCI DSS compliance requires more than documented policies. Organizations must also understand whether their technical controls effectively protect the payment environment.
Our technical security assessments can help identify vulnerabilities across systems that are within the applicable PCI DSS scope.
- External Network Security Testing
- Internal Network Security Testing
- Web Application Testing
- API Security Testing
- Configuration Review
- Vulnerability Assessment
- Segmentation Validation
- Remediation Retesting
FREQUENTLY ASKED QUESTIONS
What is PCI DSS?
PCI DSS is a security standard designed to help organizations protect payment card data and maintain appropriate security controls around cardholder data environments.
Who needs to comply with PCI DSS?
Organizations that store, process or transmit payment card data may have PCI DSS obligations. The applicable requirements depend on the organization’s role, payment environment and assessment requirements.
What is a Cardholder Data Environment?
The Cardholder Data Environment (CDE) consists of systems and components involved in storing, processing or transmitting cardholder data, along with applicable connected systems.
What does a PCI DSS Gap Assessment include?
A gap assessment reviews applicable PCI DSS requirements against your existing security controls, processes and documentation to identify areas requiring remediation.
Does PCI DSS compliance require penetration testing?
Applicable PCI DSS requirements can include technical security testing such as penetration testing. The specific testing requirements depend on the applicable scope and implementation.
Can you help with PCI DSS documentation?
Yes. We can support policies, procedures, control documentation, evidence preparation and other compliance-related documentation.
Do you provide remediation support?
Yes. We can provide prioritized remediation recommendations and work with technical teams to validate security improvements.
How often should PCI DSS controls be reviewed?
PCI DSS requires ongoing security activities, and specific testing or review frequencies depend on the applicable requirement and implementation. Organizations should maintain their security controls continuously rather than treating compliance as a one-time exercise.
RELATED SERVICES
ISO 27001 Compliance
Strengthen your information security management system and achieve compliance.
Microsoft 365 Security
Secure Microsoft 365 protects business data and reduce cloud-based security risks.
Malware Analysis
Analyze malicious software to uncover its behavior, impact, and potential security threats.