SOC 2 COMPLIANCE
Build Trust With Secure, Reliable & Auditable Systems.
Strengthen your security controls and prepare for SOC 2 with a structured approach to risk management, access control, monitoring, incident response and operational security.
Demonstrate That Your Security Controls Work
SOC 2 provides a framework for evaluating controls relevant to security and other Trust Services Criteria. Organizations use SOC 2 examinations to provide customers and stakeholders with greater visibility into how controls are designed and operated.
Our SOC 2 consulting services help organizations understand applicable requirements, assess their existing controls, identify gaps and establish a practical roadmap toward assessment readiness.
We help connect security, technology and business processes so that compliance becomes part of your organization’s day-to-day operations.
What We Do
We assess your existing security and operational controls against the applicable SOC 2 Trust Services Criteria and identify areas requiring improvement.
Our approach covers control assessment, risk management, access management, security monitoring, change management, incident response, policies, evidence preparation and audit readiness.
We work with technical and business teams to establish controls that are practical, measurable and sustainable.
How It Helps Your Business
A structured SOC 2 program helps organizations demonstrate that appropriate controls are in place to protect systems and information.
It can provide customers and stakeholders with greater transparency into your security practices while helping internal teams establish consistent processes for managing security and operational risks.
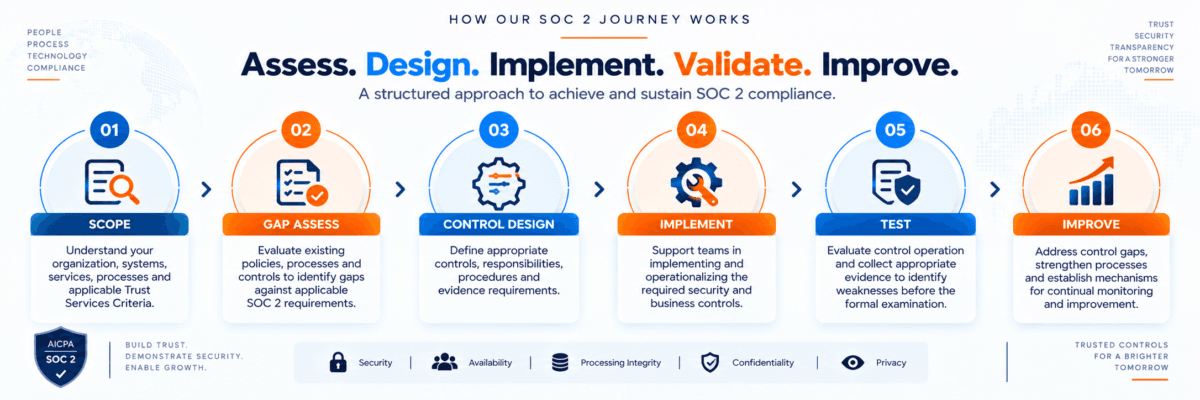
How Our SOC 2 Journey Works
Assess. Design. Implement. Validate. Improve.
SOC 2 SCOPE
SOC 2 assessments can address different Trust Services Criteria depending on the organization’s services, systems and objectives.
Security
Evaluate controls designed to protect systems and information against unauthorized access, disclosure, damage and other security threats.
Availability
Assess controls supporting the availability and operational resilience of systems and services according to defined commitments.
Processing Integrity
Evaluate whether system processing is complete, valid, accurate, timely and authorized where applicable.
Confidentiality
Assess controls designed to protect information designated as confidential throughout its lifecycle.
Privacy
Evaluate controls related to the collection, use, retention, disclosure and disposal of personal information where applicable.
Security Controls That Build Customer Confidence
Customers increasingly need visibility into how technology providers protect systems and information.
SOC 2 can provide an independent examination of relevant controls and give customers and stakeholders greater insight into an organization’s control environment.
Our approach helps organizations build that control environment around practical security and operational processes rather than treating compliance as a documentation exercise.
- Demonstrate security control maturity
- Improve customer trust and transparency
- Strengthen internal governance
- Establish repeatable operational controls
- Improve audit and evidence readiness
- Identify weaknesses before formal assessment
TESTIMONIAL
The SOC 2 readiness assessment gave our teams a clear view of our existing controls and the gaps we needed to address. The structured roadmap helped us establish consistent processes and prepare our evidence more effectively.
SOC 2 & SECURITY CONTROL RISKS
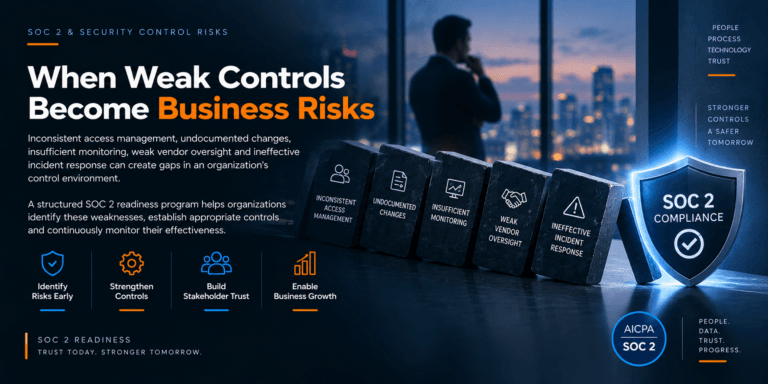
When Weak Controls Become Business Risks
FREQUENTLY ASKED QUESTIONS
What is SOC 2?
SOC 2 is an examination framework focused on controls relevant to the Trust Services Criteria. It is commonly used by service organizations to provide information about their controls to customers and other stakeholders.
What are the SOC 2 Trust Services Criteria?
The Trust Services Criteria are Security, Availability, Processing Integrity, Confidentiality and Privacy. The criteria applicable to an organization depend on the scope and objectives of its examination.
What is the difference between SOC 2 Type I and Type II?
A Type I report addresses the suitability of the design of controls at a specified point in time. A Type II report also evaluates the operating effectiveness of relevant controls over a specified period.
Do you provide SOC 2 Gap Assessments?
Yes. We assess applicable controls, identify gaps and provide a prioritized remediation roadmap.
Do you help with SOC 2 policies and documentation?
Yes. We can support the development and improvement of security policies, procedures, control documentation and related evidence processes.
Do you perform control testing?
Yes. Internal control testing can help identify weaknesses and readiness gaps before the formal examination.
Do you provide SOC 2 audit certification?
SOC 2 examinations are performed by qualified independent CPA firms. Our role can focus on readiness, control assessment, implementation support, remediation and preparation.
How long does SOC 2 readiness take?
The timeline varies based on the organization’s size, systems, scope, existing controls, selected criteria and level of control maturity.
Is SOC 2 the same as ISO 27001?
No. They are different frameworks with different structures and objectives. Organizations may use both depending on their customer, contractual and business requirements.
RELATED SERVICES
PCI DSS Compliance
Protect payment card data and strengthen security controls to meet PCI DSS requirements.
ISO 27001 Compliance
Strengthen your information security management system and achieve ISO 27001.
Red Team Assessment
Simulate real-world attacks to uncover hidden vulnerabilities and test your organization’s defenses.