ISO 27001 COMPLIANCE
Build a Secure, Auditable & Resilient Information Security Management System.
Establish, implement and continuously improve an ISO 27001-aligned Information Security Management System (ISMS) that protects critical information, manages security risks and strengthens organizational resilience.
From Information Security Risks to a Stronger ISMS
ISO 27001 provides a structured framework for managing information security through risk assessment, governance, security controls and continual improvement. Our ISO 27001 consulting services help organizations establish a practical and sustainable ISMS aligned with their business objectives.
What We Do
We help organizations assess their current information security practices, identify gaps and establish the processes required for an effective ISO.
Our approach covers information security governance, risk assessment, control implementation, documentation, employee awareness, internal auditing and management review.
We work with your teams to turn ISO 27001 requirements into practical security processes that can be maintained beyond certification.
How It Helps Your Business
A structured ISMS helps organizations identify and manage information security risks before they become incidents.
It strengthens security governance, improves accountability, supports regulatory and contractual requirements, and provides a repeatable framework for protecting information assets.
It also helps prepare your organization for internal audits, certification assessments and continual improvement.
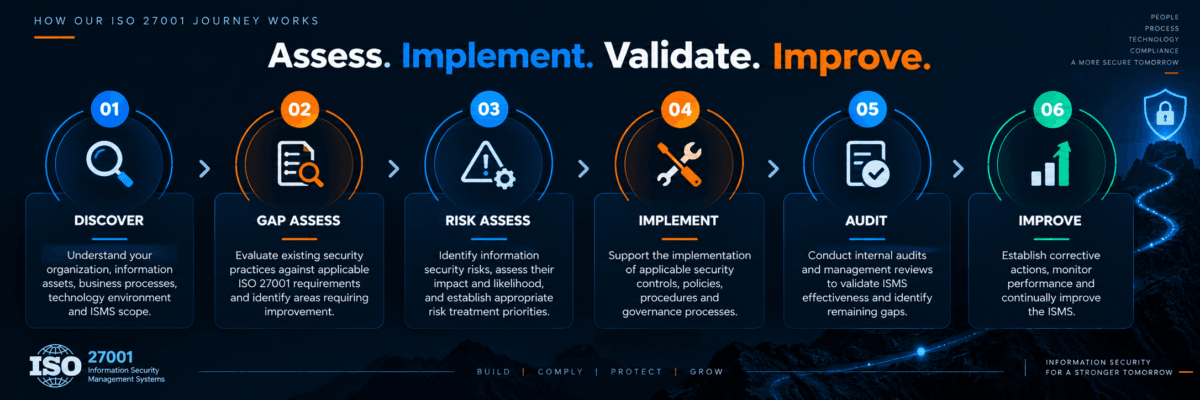
How Our ISO 27001 Journey Works
Assess. Implement. Validate. Improve.
ISO 27001 COMPLIANCE SCOPE
Your ISMS can be designed around the parts of your organization that require formal information security governance and protection.
Information Security Governance
Establish policies, responsibilities and governance processes for managing information security.
Risk Management
Identify, assess, treat and monitor information security risks across business operations.
Asset Management
Identify and manage information assets, ownership, classification and acceptable use.
Access Control
Strengthen identity, authentication and access management practices.
People & Security Awareness
Define employee security responsibilities and strengthen security awareness.
Technology & Infrastructure
Address security requirements across networks, systems, endpoints, applications and cloud environments.
Incident Management
Establish processes for detecting, reporting, responding to and learning from information security incidents.
Business Continuity
Integrate information security requirements into business continuity and resilience planning.
Turn Information Security Into a Managed Business Process
ISO 27001 is more than a collection of security controls. It provides a management framework for identifying information security risks and establishing processes to address them.
Our consulting approach helps organizations move from fragmented security practices to a structured ISMS with defined responsibilities, documented processes, measurable objectives and continual improvement.
- Structured information security governance
- Risk-based security decision making
- Defined policies and procedures
- Improved security accountability
- Better protection of sensitive information
- Stronger audit and assessment readiness
- Improved customer and stakeholder confidence
- Continual improvement of security processes

TESTIMONIAL
The ISO 27001 assessment helped us understand where our information security processes needed improvement. The structured approach gave our teams a clearer understanding of risks, responsibilities and the controls required across the organization.
ISO 27001 & INFORMATION SECURITY RISK
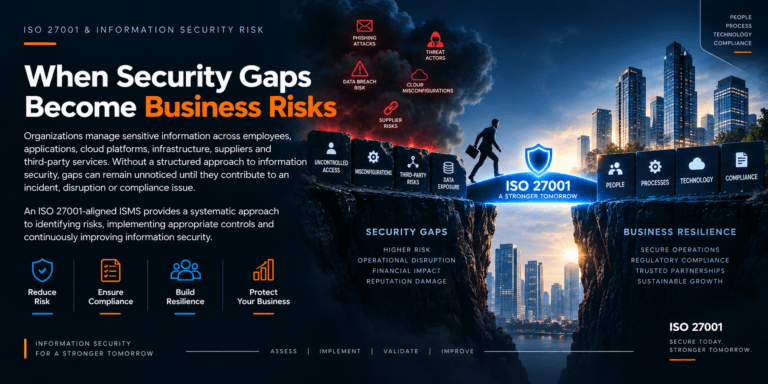
When Security Gaps Become Business Risks
FREQUENTLY ASKED QUESTION
What is ISO 27001?
ISO/IEC 27001 is an international standard for establishing, implementing, maintaining and continually improving an Information Security Management System (ISMS).
Is ISO 27001 only for IT companies?
No. Organizations across industries can implement an ISMS to manage information security risks involving people, processes, technology and third parties.
What does an ISO 27001 Gap Assessment include?
A gap assessment reviews your existing information security practices against applicable ISO 27001 requirements and identifies areas that require remediation or improvement.
How long does ISO 27001 implementation take?
The timeline depends on the organization’s size, ISMS scope, existing security maturity, resources and the level of documentation and control implementation required.
Do you help with ISO 27001 documentation?
Yes. We can support the development and improvement of policies, procedures, risk documentation, control documentation and other ISMS-related documented information.
Do you conduct internal audits?
Yes. Internal audit support can be used to evaluate ISMS conformity and effectiveness before an external certification assessment.
Can ISO 27001 help with customer security requirements?
An ISO 27001-aligned ISMS can provide a structured way to demonstrate that information security risks are being systematically managed, which can support customer, contractual and stakeholder requirements.
Does ISO 27001 certification guarantee complete security?
No. ISO 27001 establishes a risk-based management system; it does not eliminate every information security risk. The ISMS must be continually maintained and improved as threats, technology and business requirements change.
Grow your report
Incident Response
Continuously monitor, detect and respond to suspicious security activity.
RIEG
Identify and validate vulnerabilities before attackers can exploit them.
MSSP
Full managed security programme including SOC, policy, and compliance.