VULNERABILITY ASSESSMENT AND PENETRATION TESTING
Find the vulnerabilities attackers can actually exploit.
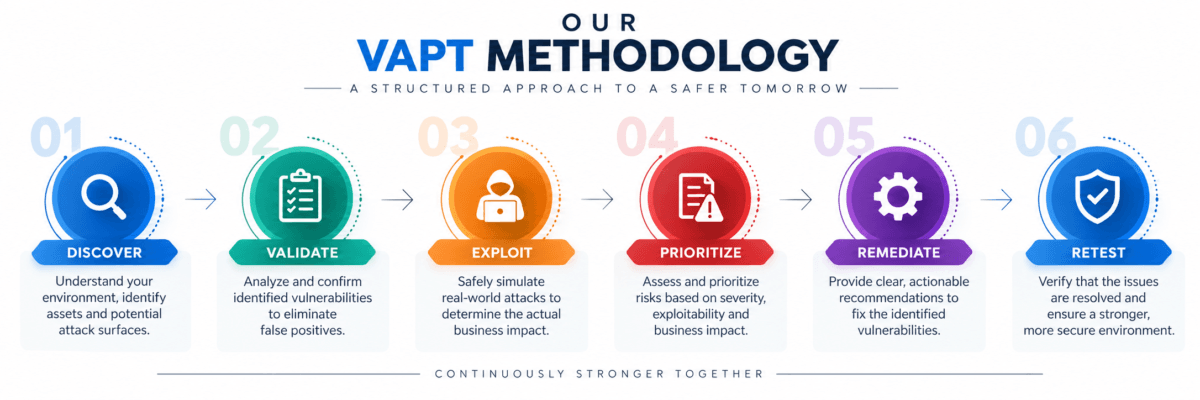
Expert-led VAPT across networks, web applications, APIs, cloud and mobile environments—with manual validation, real-world exploitation, business-impact analysis and remediation retesting.
From Vulnerabilities to Actionable Security Decisions
What We Do
We identify vulnerabilities across your attack surface, validate
their real-world impact, and provide prioritized recommendations.
What makes our VAPT different:
- Manual testing by certified penetration testers (not just automated scans)
- Real-world exploitation (we don’t just find—we prove impact)
- Business-focused reporting (findings translated to risk, not just CVE numbers)
- Remediation guidance (not just a list of problems)
Reports accepted by RBI, SEBI, CERT-In (no re-testing required)
How It Helps Your Business
Know what attackers can see, understand what they can exploit, and focus your security efforts where they matter most.
VAPT helps organizations reduce attack surface, prioritize remediation, strengthen security controls, and make informed cybersecurity decisions.
VAPT Scope Options
Network Penetration Testing
Discover vulnerabilities on your internet-facing infrastructure before attackers do.
Web Application Penetration Testing
Expose security flaws across your web applications, APIs, authentication, and business logic. Simulate sophisticated attacks based on real-world threats and OWASP security risks. Secure your applications, protect customer data, and build greater digital trust.
Cloud Infrastructure Testing
Identify cloud misconfigurations, excessive permissions, exposed services, and infrastructure weaknesses. Assess your AWS, Azure, or GCP environment against realistic attack scenarios. Reduce cloud risk, protect sensitive workloads, and strengthen your overall security posture.
Compliance Testing (PCI DSS, RBI, SEBI)
Evaluate your security controls against applicable PCI DSS, RBI, and SEBI requirements. Identify compliance gaps before they become audit findings, security incidents, or business risks. Build stronger controls and improve your readiness for regulatory and compliance assessments.
Mobile & IoT Penetration Testing
Identify vulnerabilities across mobile applications, APIs, connected devices, and IoT ecosystems. Test authentication, encryption, data storage, firmware, and communication channels for weaknesses. Protect users, devices, and connected environments from evolving cyber threats.
Post-Remediation Retesting
Verify that identified vulnerabilities have been properly fixed and securely closed. Retest affected systems to confirm remediation and ensure fixes have not introduced new risks. Gain confidence that your security improvements deliver measurable and lasting protection.
Certified, Experienced Penetration Testers
We discovered a pre-auth vulnerability in a Government Aided Company's API gateway, a privilege escalation in Active Directory, and exposed credentials in source code—all exploitable from the internet. Remediating these findings prevented an estimated $2M+ in breach risk.
- Average 23 vulnerabilities found per engagement
- 12 critical, 8 high, 3 medium per typical assessment
- 100% certifications in OSCP, CEH, GPEN, ISO 27001
- RBI & SEBI compliance expertise (India-specific).
*Based on selected VAPT engagements; findings vary according to scope, environment and assessment depth.
Testimonial
Securiglobe's penetration testers don't just find vulnerabilities— they think like attackers. They understood our infrastructure, tested realistically against our business logic, and delivered findings we could actually remediate in 48 hours. They're not here to pad a report; they're here to make us genuinely secure.
Here is what happened when a real organization hired us
Frequently Asked Questions
Will VAPT testing disrupt our production environment?
No. Testing is scheduled during agreed windows. We avoid destructive techniques on live systems. Staging/replica testing available if needed.
How long does a typical VAPT service take?
The duration of a VAPT service in India depends on the scope and complexity of the environment. A typical network VAPT takes 3 to 5 business days, while web application testing generally takes 5 to 10 business days. A precise timeline is provided after scoping.
What credentials do your VAPT testers hold?
Our VAPT testing services are delivered by certified penetration testers with credentials including OSCP, CEH, GPEN, and eWPT. Tester CVs are available on request.
Is your VAPT certificate accepted by regulators in India?
Our VAPT services in India include professionally structured reports and certificates designed to support applicable regulatory requirements, including RBI, SEBI, and CERT-In requirements, depending on the organization’s scope and regulatory obligations.
What does your VAPT service include?
Our VAPT service combines vulnerability assessment and penetration testing to identify security weaknesses across networks, web applications, APIs, cloud environments, and other in-scope assets. The assessment includes technical findings, risk ratings, evidence, and remediation recommendations.
Why choose a VAPT company in India for penetration testing?
Choosing an experienced VAPT company in India helps organizations identify exploitable vulnerabilities, strengthen their security posture, and address applicable regulatory requirements. Our VAPT services combine automated vulnerability discovery with manual penetration testing for more comprehensive security validation.
Related Services
Network Security Assessment
Deep review of network architecture and controls
SOC as a Service
Continuous monitoring to catch what VAPT snapshots miss