RBI COMPLIANCE
Strengthen Regulatory Compliance. Secure Your Financial Infrastructure.
Build stronger IT governance, cybersecurity, risk management and operational resilience aligned with applicable RBI regulatory requirements.
Build a Stronger RBI Compliance Framework
Financial institutions operate in an environment where technology, cybersecurity, data protection and operational resilience are closely connected.
Our RBI compliance services help regulated entities assess their current IT and cybersecurity posture, identify control gaps and establish a structured remediation roadmap aligned with applicable RBI directions and regulatory expectations.
The RBI’s 2023 IT Governance, Risk, Controls and Assurance framework emphasizes areas including IT governance, IT risk management, information security, business continuity/disaster recovery and assurance practices
What We do
We help organizations evaluate their IT governance, cybersecurity and risk management controls against applicable RBI regulatory requirements.
Our assessment covers policies, processes, technical controls and operational practices across the technology environment.
Our approach includes:
- RBI compliance gap assessment
- IT governance assessment
- Cybersecurity assessment
- IT risk assessment
- VAPT and security testing
- Business continuity & disaster recovery assessment
- Third-party risk assessment
- Audit and compliance readiness
How It Helps Your Business
A structured RBI compliance program helps organizations strengthen both regulatory readiness and cybersecurity resilience.
Business benefits include:
- Identify regulatory and control gaps
- Strengthen IT governance
- Reduce cybersecurity risks
- Improve operational resilience
- Strengthen incident preparedness
- Improve third-party risk visibility
- Prepare for audits and assessments
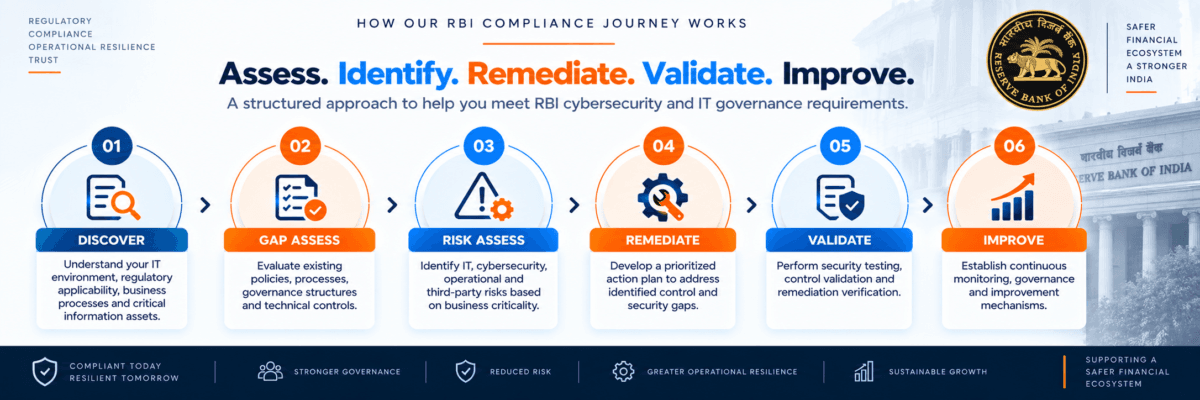
HOW OUR RBI COMPLIANCE JOURNEY WORKS
Assess. Identify. Remediate. Validate. Improve.
RBI COMPLIANCE SCOPE
Assess your technology, cybersecurity and governance controls against applicable RBI requirements.
IT Governance
Review governance structures, responsibilities, policies and management oversight for technology and information security.
Information Security
Assess security policies, access controls, information protection and security management practices.
Cybersecurity
Evaluate preventive, detective and responsive security controls across your technology environment.
IT Risk Management
Identify, assess and prioritize technology and cybersecurity risks affecting business operations.
Asset & Infrastructure Security
Assess networks, servers, endpoints, applications, cloud infrastructure and other critical technology assets.
Vulnerability Management
Evaluate vulnerability identification, remediation, patching and security testing processes.
Business Continuity & Disaster Recovery
Assess BCP, DR, backup, recovery and resilience capabilities for critical systems.
Third-Party Risk Management
Review security and risk management controls associated with technology vendors and outsourced services.
Turn Regulatory Requirements Into Stronger Security
RBI compliance should extend beyond policies and documentation.
Our approach connects regulatory requirements with practical cybersecurity assessments to help organizations understand whether their controls are effectively implemented.
We help you:
- Identify technology risks
- Assess security controls
- Validate vulnerabilities
- Strengthen governance
- Improve incident readiness
- Build audit-ready evidence
- Track remediation
TESTIMONIAL
The assessment helped us identify gaps across our IT governance and security controls. The structured recommendations gave our team a clear roadmap for improving our cybersecurity and compliance readiness.
RBI COMPLIANCE & CYBERSECURITY SECTION
Regulatory gaps can become cybersecurity risks.
FREQUENTLY ASKED QUESTIONS
What is RBI Compliance?
RBI compliance refers to meeting the regulatory requirements applicable to an organization’s specific RBI-regulated activities, including relevant requirements covering IT governance, cybersecurity, risk management and operational resilience.
Who needs RBI Compliance?
RBI compliance requirements vary according to the type of RBI-regulated entity and the activities it performs. The applicable regulatory requirements should therefore be assessed based on the organization’s specific category.
What does an RBI Compliance Assessment cover?
It can include IT governance, cybersecurity, IT risk management, information security, vulnerability management, business continuity, disaster recovery and third-party risk management.
Does RBI Compliance include VAPT?
Where applicable, vulnerability assessment and penetration testing can form part of the organization’s cybersecurity assessment and compliance program.
Do you provide RBI Gap Assessments?
Yes. We assess applicable requirements against existing policies, processes, governance structures and technical controls and provide a prioritized remediation roadmap.
Can you help prepare compliance documentation?
Yes. We can support policy and procedure reviews, control documentation, assessment reports, evidence preparation and remediation tracking.
Does RBI Compliance only involve documentation?
No. Effective compliance involves governance, processes, controls and technical validation—not documentation alone.
RELATED SERVICES
ISO 27001 Compliance
Build a structured Information Security Management System and strengthen information security governance.
SOC 2 Compliance
Strengthen security, availability, confidentiality and operational controls to build customer trust.
VAPT
Identify, validate and prioritize vulnerabilities across your applications, infrastructure and networks.
Strengthen Your RBI Compliance & Cybersecurity Readiness Identify gaps, strengthen controls and build a more resilient technology environment.