RBI COMPLIANCE
Strengthen Regulatory Compliance. Secure Your Financial Infrastructure.
Build stronger IT governance, cybersecurity, risk management and operational resilience aligned with applicable RBI regulatory requirements.
Build a Stronger RBI Compliance Framework
Financial institutions operate in an environment where technology, cybersecurity, data protection and operational resilience are closely connected.
Our RBI compliance services help regulated entities assess their current IT and cybersecurity posture, identify control gaps and establish a structured remediation roadmap aligned with applicable RBI directions and regulatory expectations.
The RBI’s 2023 IT Governance, Risk, Controls and Assurance framework emphasizes areas including IT governance, IT risk management, information security, business continuity/disaster recovery and assurance practices
What We do
- RBI Compliance Gap Assessment: Assess your existing IT, cybersecurity and governance controls against applicable RBI requirements.
- IT Governance Assessment: Review governance structures, responsibilities, policies, committees and management oversight.
- Cybersecurity & Information Security Assessment: Evaluate security controls protecting critical systems, applications, infrastructure and information assets.
- IT Risk Assessment: Identify technology-related threats, vulnerabilities, risks and control weaknesses.
- VAPT & Security Testing: Perform vulnerability assessment and penetration testing across applicable networks, applications, APIs, cloud environments and infrastructure.
- Business Continuity & Disaster Recovery: Assess BCP and DR capabilities to support operational resilience and recovery.
- Third-Party Risk Assessment: Review security and risk management practices associated with technology vendors and service providers.
- IT Audit & Compliance Readiness: Prepare organizations for internal, regulatory and independent technology assurance activities
How It Helps Your Business
- Regulatory Readiness: Understand applicable RBI requirements and identify areas requiring remediation.
- Stronger IT Governance: Improve accountability, oversight and decision-making around technology and cyber risk.
- Reduced Cyber Risk: Identify vulnerabilities and control weaknesses before they become operational or security incidents.
- Improved Resilience: Strengthen business continuity, disaster recovery and incident response capabilities.
- Better Audit Preparedness: Maintain evidence, documentation and security controls required for assurance activities.
- Third-Party Visibility: Identify and manage cybersecurity risks introduced through technology vendors and service providers.
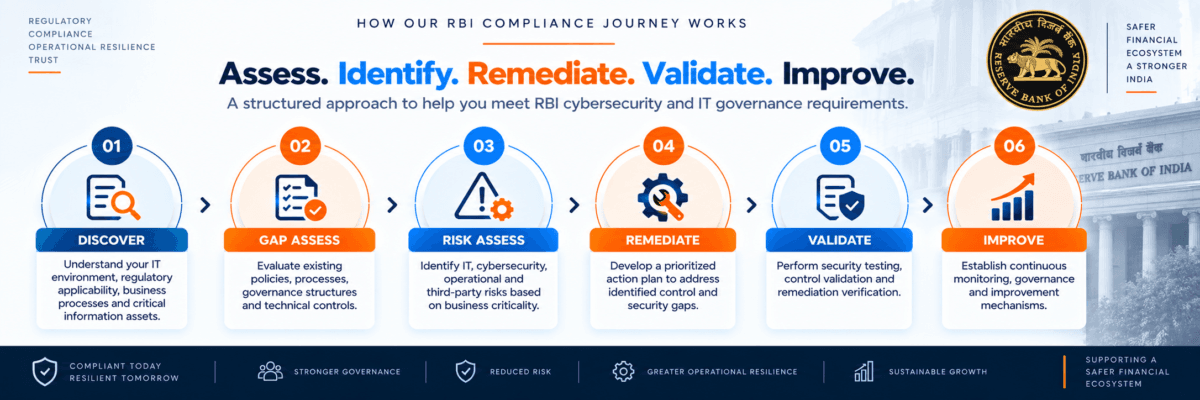
HOW OUR RBI COMPLIANCE JOURNEY WORKS
Assess. Identify. Remediate. Validate. Improve.