How a Managed Security Service Provider (MSSP) Stopped a Multi-Stage Ransomware Attack Before Encryption
Introduction
Modern ransomware operations are no longer single-stage attacks. They are carefully orchestrated intrusion campaigns that combine phishing, credential theft, privilege escalation, defense evasion, and lateral movement before encryption is ever attempted.
For defenders, the challenge is not identifying ransomware after it executes—it’s detecting the subtle behavioral indicators that precede it.
In one incident investigated by an MSSP, the earliest evidence consisted of a suspicious parent-child process relationship, an anomalous Azure AD authentication event, and encrypted outbound traffic to an infrastructure that had no prior reputation. None of these indicators were conclusive on their own. Together, they formed a high-confidence attack narrative that enabled the SOC to contain the intrusion before the ransomware payload could be deployed.
This article walks through the investigation from the analyst’s perspective, highlighting the telemetry, detection logic, and response actions that prevented a full-scale compromise.
Stage 1 — Initial Access
The attack began with a phishing email impersonating a logistics partner.
Subject:
Updated Shipping Invoice
The attachment:
Invoice_July_2026.docm
When opened, no macro prompt appeared.
Instead, the document exploited a recently disclosed Office vulnerability to spawn:
WINWORD.EXE

↓

powershell.exe
Command observed:
powershell.exe -ExecutionPolicy Bypass -EncodedCommand SQBmACg...
The encoded command downloaded a second-stage payload from:
hxxps://cdn-storage-sync[.]com/update.bin
No antivirus signatures detected the payload.
The binary had never been submitted to VirusTotal.
Static detection failed.
Behavioral monitoring became the only reliable indicator.
Stage 2 — Endpoint Detection
The MSSP’s EDR platform immediately generated telemetry showing unusual parent-child relationships:
WINWORD.EXE

↓

powershell.exe

↓

rundll32.exe

↓

svchost.exe
Normal Office activity rarely launches PowerShell.
Even more unusual:
PowerShell attempted:
- Disable AMSI
- Modify Windows Defender exclusions
- Download additional payloads
- Inject shellcode into memory
Behavior-based analytics assigned the process chain a high confidence score.
The endpoint was automatically elevated for investigation.
Stage 3 — SIEM Correlation
At this stage, individual alerts were fed into the SIEM.
The correlation engine connected:
Identity Logs
Azure AD Login

Country:

Netherlands

Previous Login:

India

Difference:

4 minutes

Impossible Travel detected.
Endpoint Logs
Encoded PowerShell

AMSI bypass

Memory Injection
Firewall Logs
Outbound TLS connection

Unknown reputation

Rare destination

Port 443
DNS Logs
TXT Record Queries

Multiple random subdomains

High entropy domains

Possible C2 beaconing.
Microsoft Defender Events
Defender Disabled

Real-time protection turned off

Tamper attempt detected
Separately, these alerts might not trigger a major response.
Correlated together, the SIEM classified the incident as:
Potential Human-Operated Ransomware
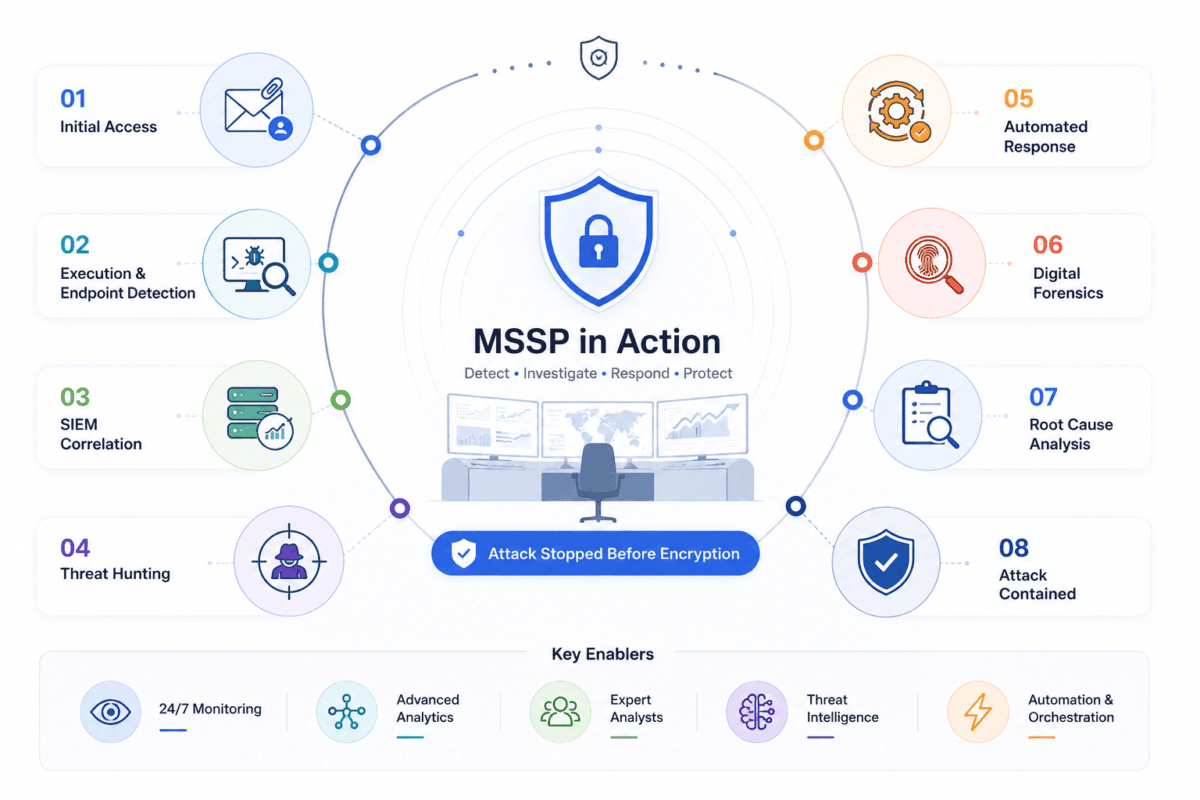
Stage 4 — Threat Hunting Begins
Rather than waiting for additional alerts, the MSSP’s threat hunting team searched the environment.
Queries included:
PowerShell executions containing:
-EncodedCommand
Scheduled tasks created within the previous hour.
New administrator accounts.
Remote Service Creation.
PsExec execution.
SMB administrative shares.
WMI event subscriptions.
Registry persistence:
HKCU

Run

RunOnce
Within minutes they discovered:
Three additional workstations had communicated with the same command-and-control server.
The attackers were already moving laterally.
Stage 5 — Lateral Movement
Network telemetry revealed repeated authentication attempts using:
SMB

WinRM

Remote WMI
Windows Security Logs showed:
4624

4625

4672
Multiple privileged logons appeared from the compromised workstation.
Soon afterward:
PsExec.exe

Remote Service Control

ADMIN$

IPC$
The attacker had obtained administrative credentials.
MITRE ATT&CK mapping:
- T1021 Remote Services
- T1078 Valid Accounts
- T1550 Pass-the-Hash
T1569 Service Execution
Stage 6 — Automated Response
The MSSP’s SOAR platform executed predefined containment playbooks.
Within seconds:
✅ Endpoint isolated
✅ User account disabled
✅ Azure AD refresh tokens revoked
✅ Firewall blocked malicious IP addresses
✅ DNS sinkhole updated
✅ IOC distributed across all endpoints
Simultaneously:
- Incident ticket created
- SOC analyst notified
- Customer informed
- Memory acquisition initiated
Automation reduced response time from potentially hours to under one minute.
Stage 7 — Digital Forensics
Memory analysis identified:
Cobalt Strike Beacon
Sleep:
45 seconds

HTTP GET Beacon

Encrypted configuration
Additional findings:
Credential dumping activity
LSASS memory access
Reflective DLL Injection
Persistence via Scheduled Tasks
Multiple encrypted payloads staged but never executed
Because containment occurred before execution, the ransomware encryption module was never launched.
Stage 8 — Root Cause Analysis
The intrusion timeline looked like this:
02:11

Phishing email delivered

↓

02:14

Malicious document opened

↓

02:15

PowerShell payload executed

↓

02:16

Command-and-Control established

↓

02:18

Credential theft

↓

02:22

Lateral movement

↓

02:29

Endpoint isolated

↓

02:30

IOC blocking deployed

↓

02:31

Incident contained
The attackers spent less than twenty minutes inside the network.
Without continuous monitoring, they would likely have remained undetected long enough to deploy ransomware across the environment.
Why the MSSP Made the Difference
The attack wasn’t stopped by a single security product. It was stopped by correlation, context, and coordinated response.
A signature-based antivirus missed the payload because it was previously unseen. The breakthrough came when the MSSP combined endpoint telemetry, identity logs, firewall events, DNS activity, and cloud authentication data to reconstruct the attack chain in real time.
Behavioral analytics exposed suspicious parent-child process relationships. SIEM correlation linked isolated alerts into a coherent incident. Threat hunters proactively searched for signs of lateral movement before encryption began. Finally, SOAR automation executed containment actions within seconds, dramatically reducing the attacker’s opportunity to escalate.
This layered approach transformed what could have become a business-disrupting ransomware event into a contained security incident.
Final Thoughts
Modern ransomware campaigns rarely begin with encryption they begin with stolen credentials, malicious PowerShell, covert persistence, and lateral movement. By the time ransom notes appear, the attacker has often spent hours or days establishing control.
An effective MSSP detects these early indicators through continuous monitoring, advanced analytics, and experienced SOC analysts who understand attacker behavior rather than relying solely on signatures. The combination of SIEM, EDR, XDR, threat intelligence, and automated response provides organizations with the visibility and speed needed to interrupt the attack before critical systems are impacted.
For organizations facing increasingly sophisticated adversaries, an MSSP is more than an outsourced monitoring service it is a continuously operating cyber defense capability designed to identify, investigate, and contain threats before they become breaches.